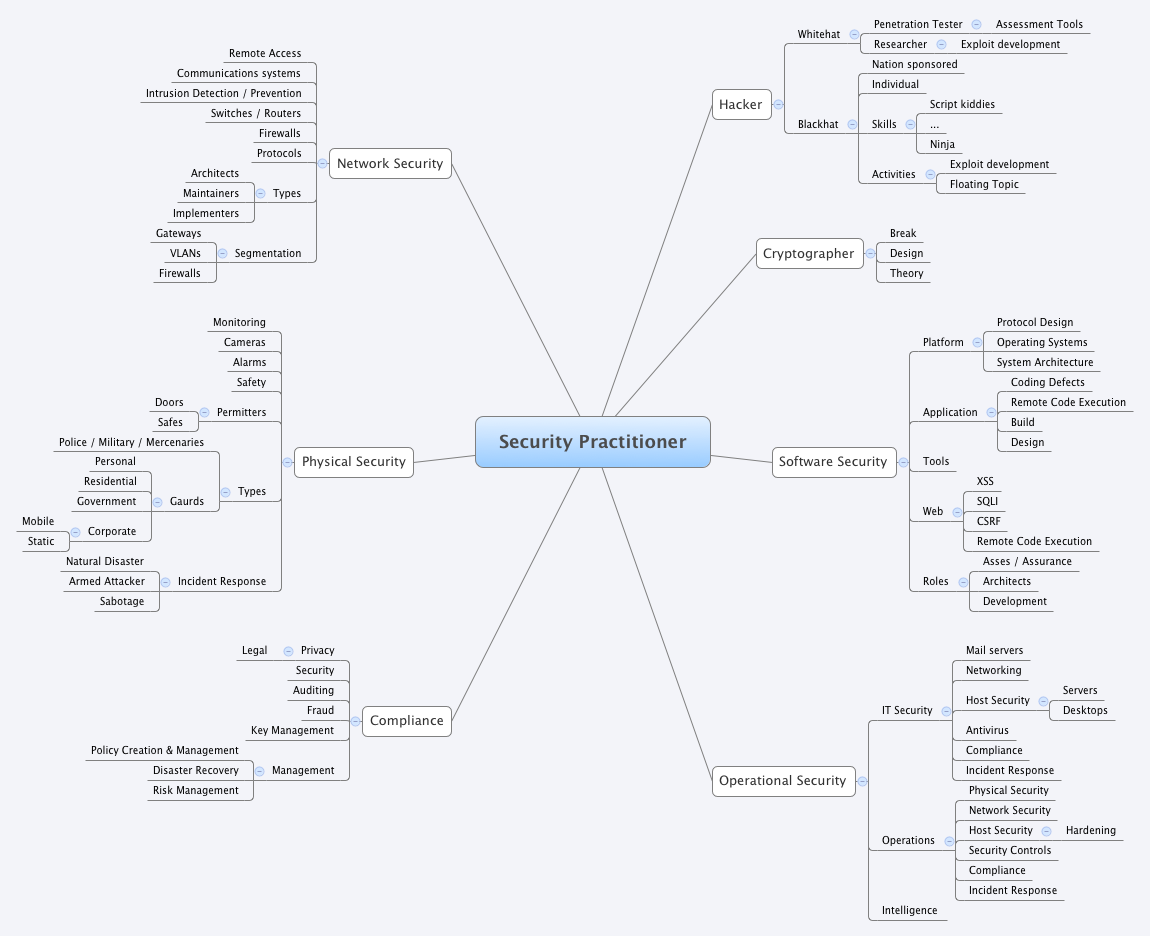
Beyond Builders, Defenders, and Breakers
This post is from 2014. Some details, links, and recommendations may be out of date.
There are lots of different types of Security Practitioners out there. At a high level they can all be thought of as Builders, Defenders or Breakers.
Another taxonomy commonly used categorizes them into more role-focused categories:
- Operations Security (OPSEC)
- Communications security (COMSEC)
- Counter-intelligence
- Information security (INFOSEC)
- Signal Security (SIGSEC)
- Transmission security (TRANSEC)
Unfortunately neither of these taxonomies does an effective job at expressing areas of focus nor skill-set.
That is not to say these taxonomies are not valuable but the leave me wanting. It also seems if I tell someone I work in “computer security” they either immediately ask me if I can hack someone’s Facebook account or they ask me about what antivirus they should run; this of course isn’t how I think about security either.
So how do I think about security practitioners? I try to categorize them based on their areas of specialty and professional focus and for me this looks something like this the bellow mind-map.